If you work in Texas higher education, there is a good chance you have sent a document to a PaperCut printer this week. The print management software runs in schools, libraries, computer labs and government offices everywhere. On Aug. 27, PaperCut confirmed attackers were exploiting a flaw that lets them take over its server without logging in.
What happened
The attack chains two bugs:
- CVE-2026-81578 is an authorization mix-up. A crafted request makes the server show one page but run an action from another, and it checks permissions for the wrong one. That lets an attacker change server settings without a login.
- CVE-2026-82078 is in PaperCut's database utilities, which can be tricked into loading unsafe Java code. Combined with the first bug, that becomes remote code execution.
Huntress found exploitation in two customer environments and reproduced the full chain against a clean install. The response got messy fast. PaperCut shipped two emergency patches within about a day after watchTowr found multiple bypasses of the first one. CISA added the flaw to its Known Exploited Vulnerabilities catalog.
The second wave got more hands-on. PaperCut documented attackers installing the SimpleHelp remote support tool as a Windows service named "Remote Access Service," then adding AnyDesk for persistence. Because these are legitimate tools, nothing on the server looks like malware.
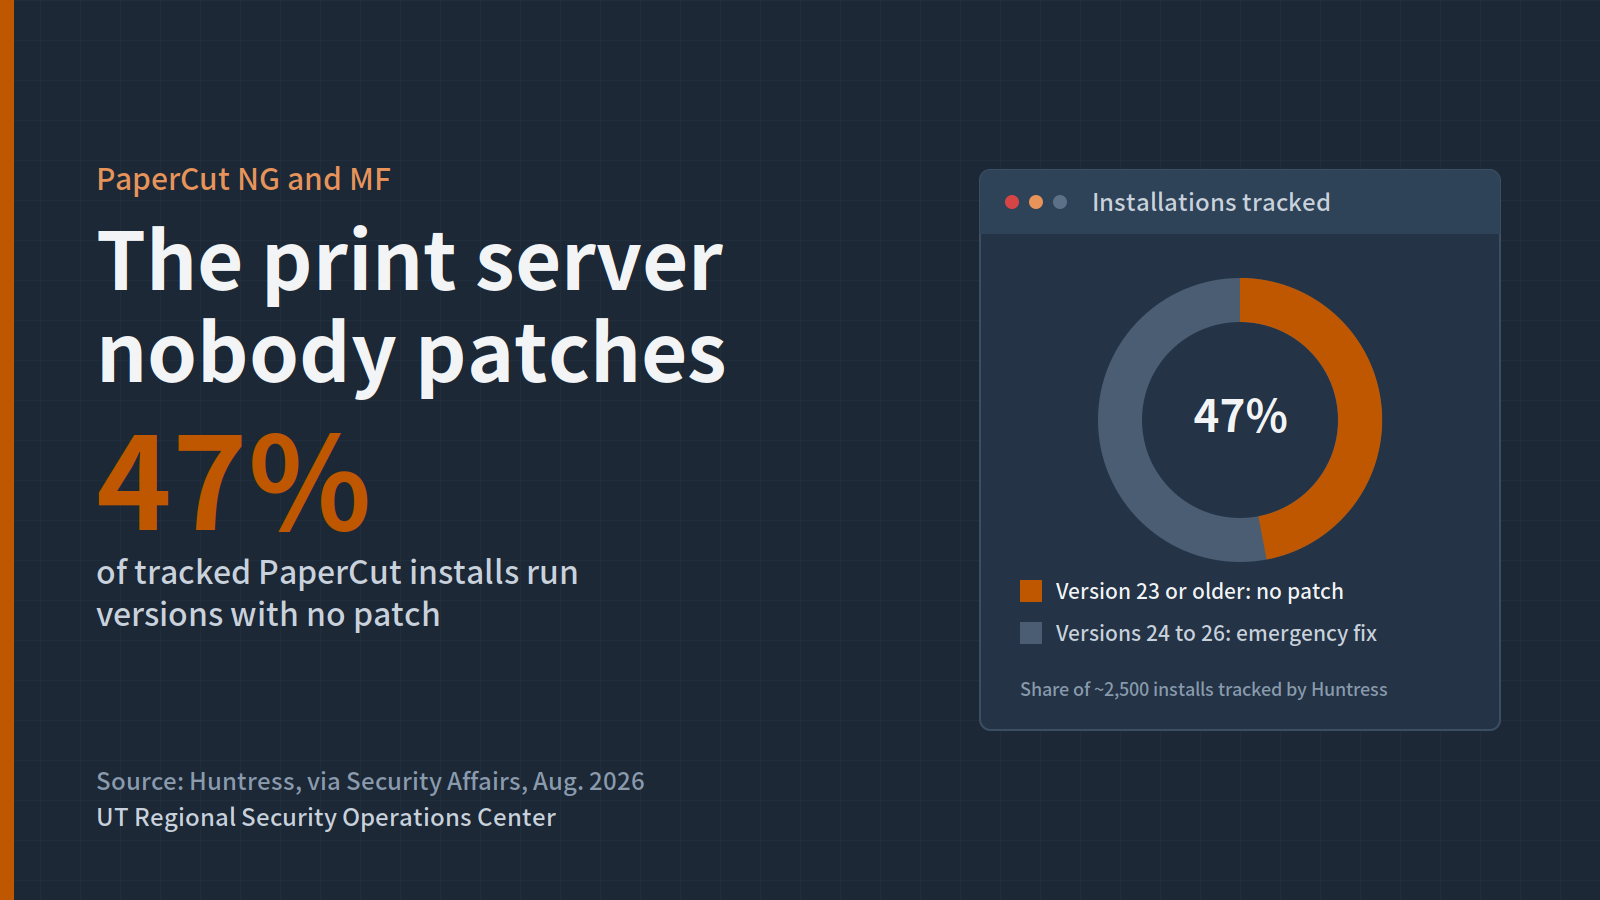
The biggest problem is age. Huntress reports that about 47% of the roughly 2,500 PaperCut installations it tracks run version 23 or older, and those versions have no patch.
Why it matters for Texas institutions
Print servers are the definition of "set it and forget it." They often run with elevated privileges, store copies of sensitive documents, and get left out of EDR coverage because they are "just the print server." On campuses, PaperCut is frequently managed by a library, lab or departmental IT group rather than central IT, which makes version drift common.
watchTowr's guidance is blunt: any PaperCut server that was internet-facing and unpatched should be assumed compromised, and patching alone will not remove an attacker already inside.
What your institution should do
- Find every PaperCut server. Check departments, libraries and labs, not just central IT.
- Patch to the latest emergency release. Fixes exist for the v24, v25 and v26 branches.
- Plan an upgrade for v23 and older. Until then, isolate those servers so only print clients and admins can reach them.
- Take the admin interface off the internet. There is rarely a good reason for it to be public.
- Hunt for remote access tools. Look for SimpleHelp, a service called "Remote Access Service," and AnyDesk on print servers.
- Put EDR on print servers. Treat them like any other privileged Windows server.
RSOC is here to help
RSOC can scan for exposed PaperCut instances, check versions, and help hunt for the remote access tools seen in these attacks. Contact rsoc@utexas.edu.
Sources: Huntress · Security Affairs · Help Net Security · NexusTek · eBuilder Security